LoginPress Pro Limit Login Attempts Addon
 Premium
Introduction
The Limit Login Attempts addon from LoginPress Pro is a security solution designed to protect your WordPress site against brute force attacks. WordPress does not limit login attempts by default, leaving your site vulnerable to automated scripts that test thousands of username and password combinations. This plugin closes that security gap in a simple and effective way.
Developed by WPBrigade, the team behind LoginPress, this addon integrates perfectly with the main LoginPress plugin and adds a robust layer of protection without requiring technical knowledge. It is aimed at WordPress site administrators, agencies, freelancers, and online store owners who want to secure their login area against intrusion attempts.
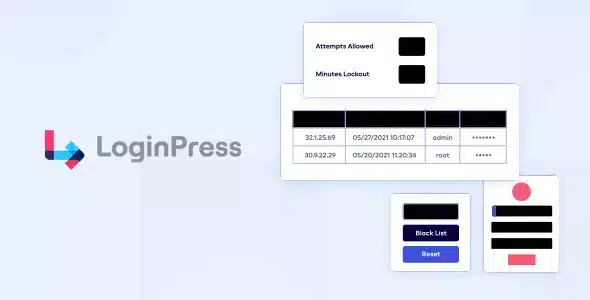
With this addon, you can configure the maximum number of allowed login attempts before a user or IP address is temporarily blocked. You can also set the block time in minutes, effectively deterring automated scripts. Additionally, it includes advanced features such as IP whitelist and blacklist, automatic blocking of suspicious usernames, disabling XML-RPC, limiting concurrent sessions, and protecting REST endpoints that expose user information.
The Attempt Details panel gives you a complete log of each failed attempt, showing the IP address, date and time, username, password used, and the access gateway (WordPress login, WooCommerce, or widget). From there, you can unblock, whitelist, or blacklist any user or IP with a single click. You can also configure email notifications to receive alerts when the attempt limit is reached, as well as customize the error messages that blocked users see.
This addon is ideal for those looking for a practical and hassle-free security solution, complementing the visual customization offered by LoginPress Pro. With its intuitive interface and simple setup, it protects your site without sacrificing user experience.
Similar items
 Premium

 Premium
 Premium